1. What is CloudHSM?
AWS CloudHSM provides dedicated single-tenant Hardware Security Modules. Unlike KMS, YOU manage the keys — AWS manages only the hardware.
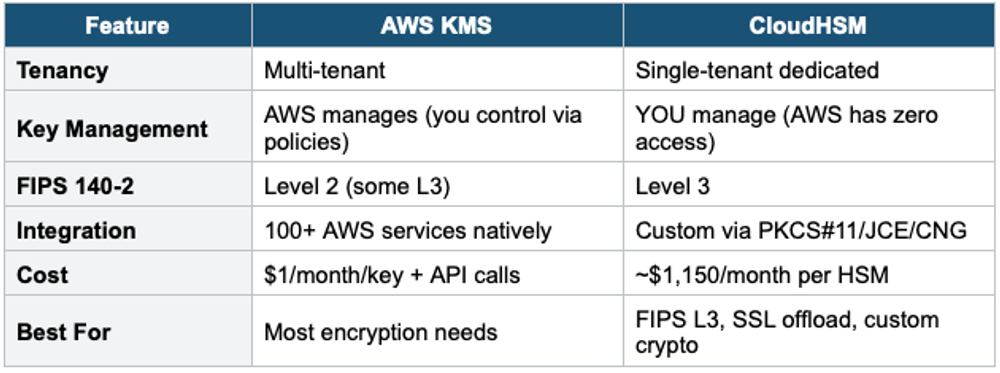
KMS vs CloudHSM
KMS = multi-tenant, AWS manages HSM, integrated with 100+ services, simpler. CloudHSM = single-tenant, YOU manage keys, FIPS 140-2 Level 3, custom crypto operations.
2. Key Characteristics
- Dedicated single-tenant HSM hardware
- YOU manage keys — AWS has NO access to key material
- FIPS 140-2 Level 3 (KMS = Level 2 with some Level 3)
- APIs: PKCS#11, JCE, CNG (industry standard)
- Deployed in your VPC. Deploy 2+ AZs for HA.
- ~$1.60/hour per HSM (~$1,150/month)
- Can integrate with KMS via Custom Key Store
3. KMS vs CloudHSM
4. Use Cases
- FIPS 140-2 Level 3 compliance
- SSL/TLS offload from web servers
- Certificate Authority private key storage
- Oracle Transparent Data Encryption (TDE)
- KMS Custom Key Store (CloudHSM as KMS backend)
Important Warning
If you lose all CloudHSM instances AND no backup, keys are PERMANENTLY LOST. AWS cannot recover them. Always maintain backups and deploy across multiple AZs.
Exam Tip
CloudHSM: "FIPS 140-2 Level 3" = CloudHSM. "Full key control" = CloudHSM. "SSL/TLS offload" = CloudHSM. "Dedicated HSM" = CloudHSM. ~$1,150/month. KMS Custom Key Store = CloudHSM backend for KMS.