1. Defense in Depth
Infrastructure protection uses multiple overlapping security layers. If one layer fails, the next layer catches the threat. This is the defense-in-depth principle applied to AWS.
Defense in Depth Layers on AWS:

Layer 1: EDGE
  CloudFront, Shield, WAF, Route 53 DNS Firewall
  → Block DDoS, bad bots, and malicious requests at the edge

Layer 2: VPC PERIMETER
  Internet Gateway, NAT Gateway, NACLs, VPC endpoints
  → Control what enters/leaves the VPC

Layer 3: SUBNET
  Public/Private subnet isolation, NACLs per subnet
  → Segment by tier (web, app, data)

Layer 4: INSTANCE / CONTAINER
  Security Groups, IAM roles, SSM Agent (no SSH)
  → Control per-resource access

Layer 5: APPLICATION
  Cognito auth, API Gateway throttling, WAF rules
  → Protect the application layer

Layer 6: DATA
  KMS encryption, Macie classification, S3 policies, Object Lock
  → Protect the data itself
2. Edge Protection
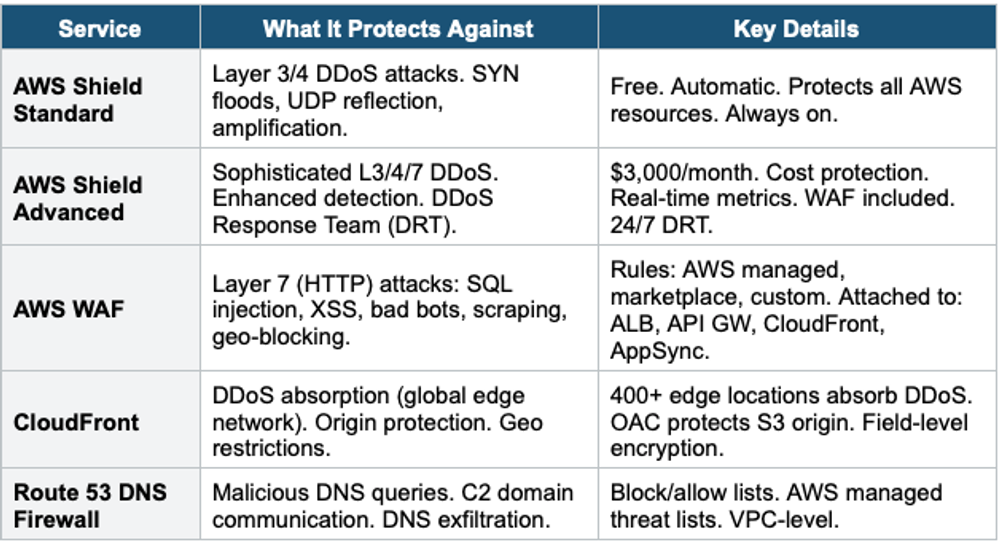
Shield Standard vs Advanced Shield Standard: free, automatic L3/4 DDoS protection for all AWS customers. Shield Advanced: paid ($3K/mo), adds: L7 DDoS protection, DDoS Response Team (DRT), cost protection (AWS credits for scaling during attack), enhanced metrics, WAF included at no extra cost. Exam: "DDoS cost protection" or "DRT access" = Shield Advanced.
3. WAF Rules Deep Dive
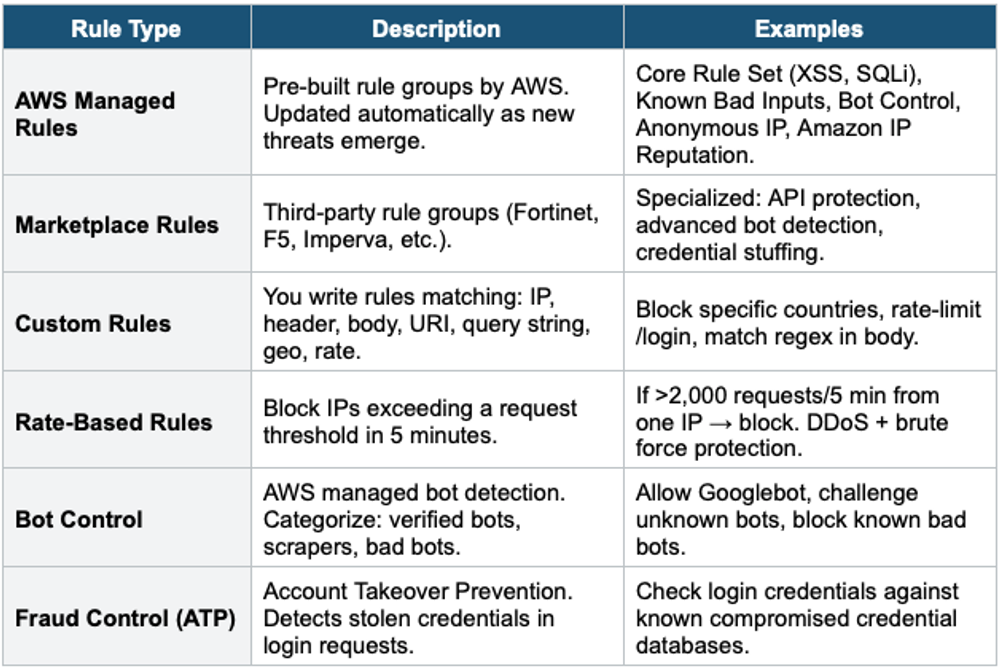
- WAF Web ACL: a collection of rules evaluated in order of priority. Action per rule: Allow, Block, Count, CAPTCHA.
- Web ACL capacity: 5,000 WCU (Web ACL Capacity Units). Each rule consumes WCUs.
- WAF Logs: full logs to S3, CloudWatch Logs, or Kinesis Firehose for analysis.
- WAF attaches to: CloudFront (global), ALB (regional), API Gateway (regional), AppSync, Cognito.
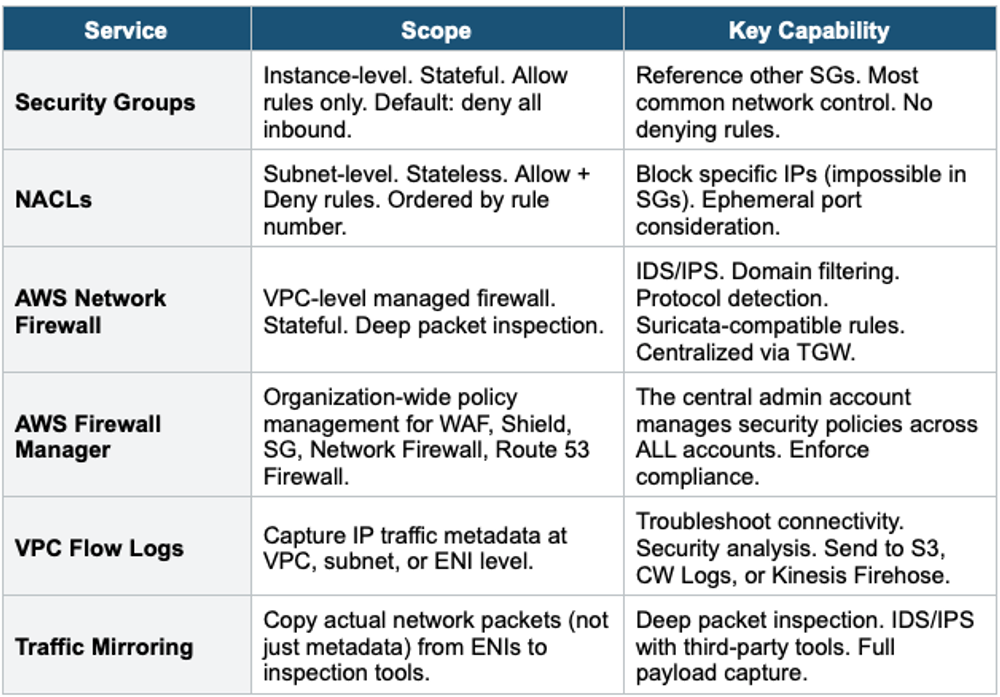
4. Network Protection
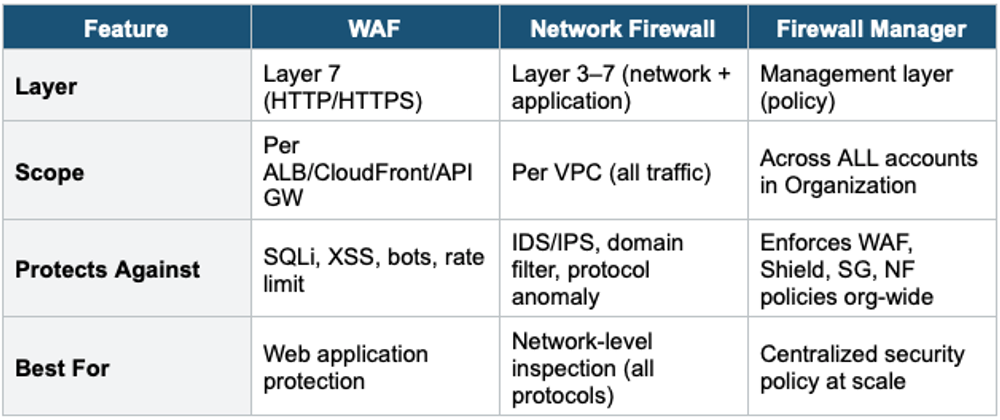
Firewall Manager vs WAF vs Network Firewall
5. Compute Protection
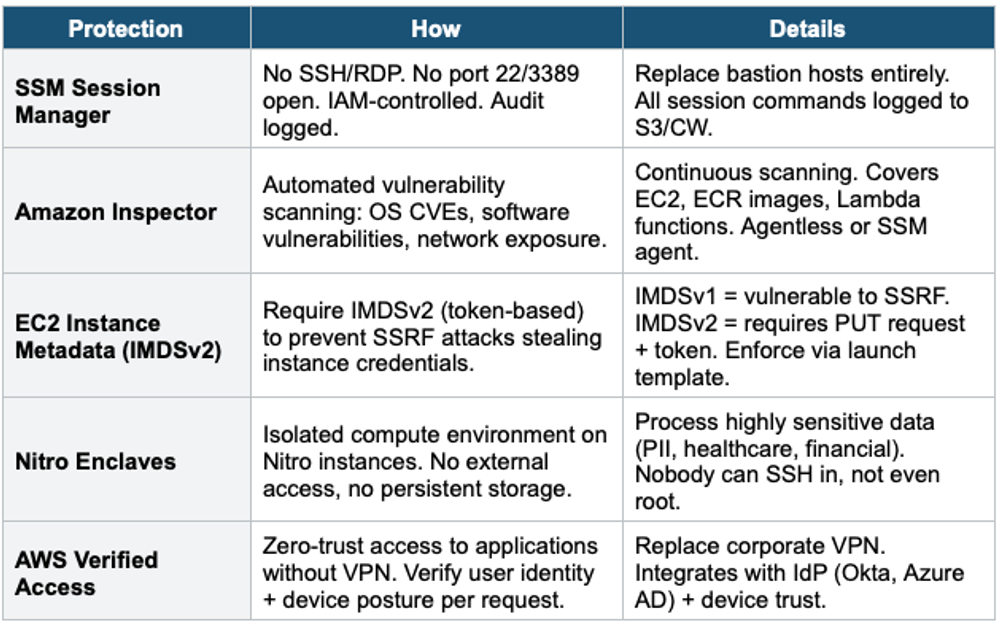
Important Warning IMDSv1 is a critical security risk. SSRF attacks can steal IAM role credentials from the metadata service (169.254.169.254). Always enforce IMDSv2 (HttpTokens=required in launch template). This prevents SSRF-based credential theft and is a frequent exam topic.
6. Complete Infrastructure Protection Decision Table
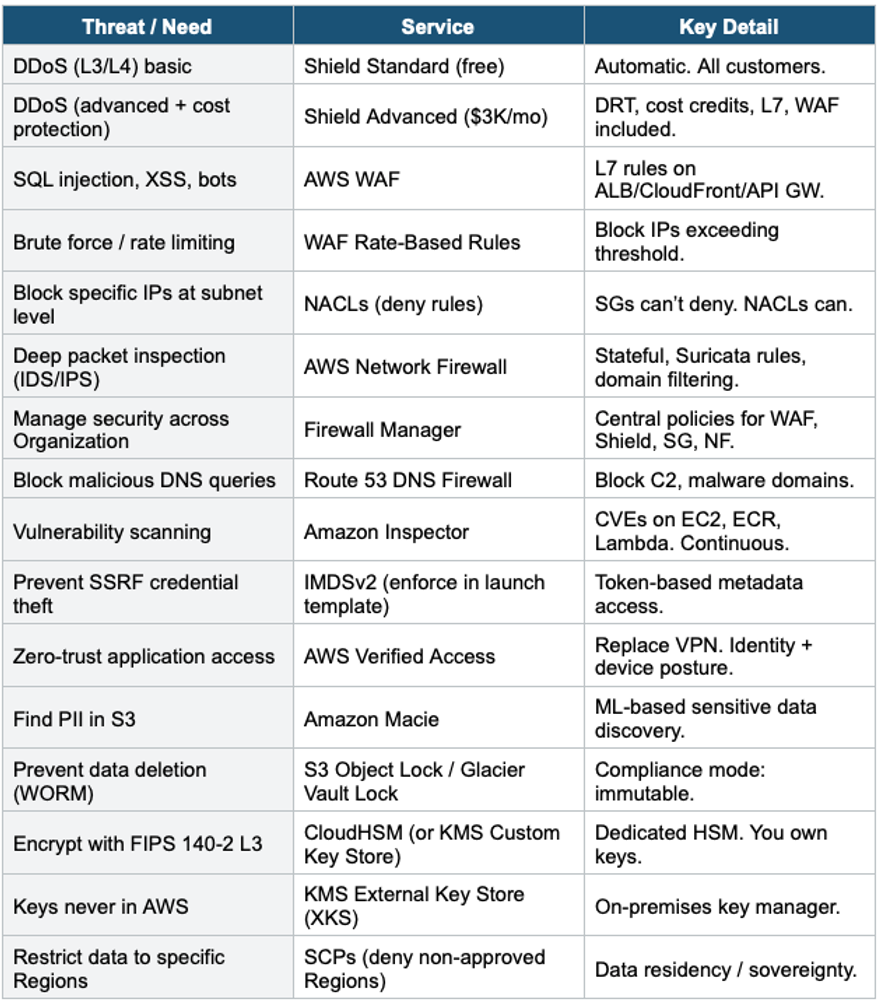
Exam Tip Infrastructure Protection: "DDoS free" = Shield Standard. "DDoS DRT + cost protection" = Shield Advanced. "L7 web attacks" = WAF. "IDS/IPS" = Network Firewall. "Manage org-wide" = Firewall Manager. "Block IPs" = NACLs (SGs can’t deny). "Vulnerability scan" = Inspector. "SSRF prevention" = IMDSv2. "Find PII" = Macie. "WORM" = Object Lock. "FIPS 140-2 L3" = CloudHSM. "Zero trust" = Verified Access. "Data residency" = SCP Region restrict.