1. TGW Deep Dive
Transit Gateway (TGW) is a regional network hub that connects VPCs, VPN connections, and Direct Connect gateways through a central point. This lesson covers advanced patterns beyond basic hub-and-spoke.
Why TGW Matters Without TGW: connecting 10 VPCs requires 45 peering connections (full mesh). Adding an 11th VPC = 10 more connections. With TGW: each VPC connects ONCE to TGW. Adding the 11th = 1 more attachment. TGW also enables transitive routing, centralized inspection, and hybrid connectivity — all from one hub.
2. TGW Route Tables
TGW route tables control which attachments can communicate with each other. This is the primary mechanism for network segmentation.
TGW Route Table Segmentation:

  TGW Attachments:
    VPC-Prod, VPC-Dev, VPC-Shared, VPC-Security, VPN-OnPrem

  Route Table: Prod-RT
    Associated: VPC-Prod
    Routes: VPC-Shared, VPC-Security, VPN-OnPrem
    (Prod can reach Shared, Security, On-Prem. NOT Dev.)

  Route Table: Dev-RT
    Associated: VPC-Dev
    Routes: VPC-Shared, VPN-OnPrem
    (Dev can reach Shared, On-Prem. NOT Prod, NOT Security.)

  Route Table: Shared-RT
    Associated: VPC-Shared
    Routes: VPC-Prod, VPC-Dev, VPC-Security, VPN-OnPrem
    (Shared can reach everyone — it provides shared services.)

  Result: Prod and Dev are isolated. Both reach Shared and On-Prem.
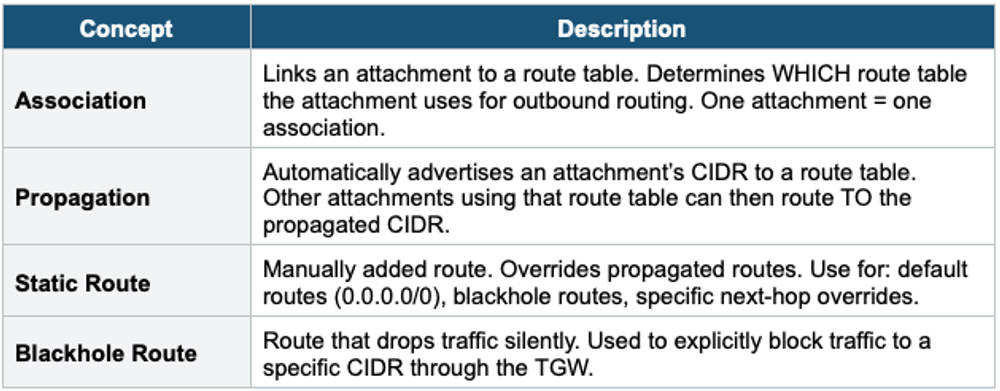
Route Table Concepts
3. Centralized Inspection Pattern
Centralized Inspection via TGW:

  VPC-A (spoke)  VPC-B (spoke)  VPN-OnPrem
       \              |              /
        \             |             /
         Transit Gateway (hub)
              |
         Inspection VPC
           |        |
      AWS Network    Third-Party
      Firewall       Appliance
           |
       [inspect + allow/deny]
           |
         Return to TGW
           |
       Destination VPC or Internet

  How: TGW appliance mode enabled.
  All inter-VPC traffic is routed through the Inspection VPC.
  Inspection VPC runs firewalls (AWS Network Firewall or Palo Alto, etc.).
Appliance Mode
- Enable on TGW VPC attachment for the Inspection VPC
- Ensures symmetric routing: return traffic goes back through the SAME firewall instance
- Without appliance mode, return traffic might go to a different AZ’s firewall, causing asymmetric routing and dropped connections
- Required for: any inspection/firewall VPC pattern
4. TGW + Direct Connect Integration
TGW + DX Integration:

  On-Premises
       |
  Direct Connect
       |
  DX Gateway (global)
       |
  Transit VIF (VLAN)
       |
  Transit Gateway (regional)
       |
  ┌─────┼─────┼─────┐
  VPC-A  VPC-B  VPC-C  ...

  One Transit VIF → DX Gateway → TGW → ALL VPCs
Much simpler than one Private VIF per VPC.- Transit VIF connects DX to TGW via DX Gateway
- One Transit VIF replaces many Private VIFs (one per VPC)
- Allowed prefixes: configure which VPC CIDRs are advertised to on-premises via BGP
- Maximum: 20 prefixes per Transit VIF (aggregate CIDRs to stay under limit)
- DX Gateway can connect to TGWs in different Regions (multi-Region hybrid via one DX)
5. TGW Cross-Region Peering
TGW Cross-Region Peering:

  Region A (us-east-1)         Region B (eu-west-1)

  TGW-A                        TGW-B
    |                            |
  VPC-1, VPC-2                VPC-3, VPC-4
  VPN-OnPrem                  VPN-Europe

  TGW-A <── peering attachment ──> TGW-B

  VPC-1 can reach VPC-3 via: TGW-A → Peering → TGW-B → VPC-3
  On-Prem can reach VPC-4 via: VPN → TGW-A → Peering → TGW-B → VPC-4

Static routes required (no propagation across peering).- Connects TGWs in different AWS Regions
- Enables global transitive routing: on-premises → TGW-A → peering → TGW-B → VPC in Region B
- Static routes only (BGP propagation does not work across TGW peering)
- Encrypted with AES-256 automatically
- Use for: multi-Region architectures, global hybrid networks, DR routing
6. TGW + VPN: ECMP
ECMP (Equal-Cost Multi-Path) A single Site-to-Site VPN connection = 2 tunnels x 1.25 Gbps = 2.5 Gbps max. With TGW, you can attach MULTIPLE VPN connections and enable ECMP to aggregate bandwidth. 4 VPN connections = up to 10 Gbps aggregate. ECMP distributes traffic across all tunnels. Use when you need more VPN bandwidth than a single connection provides.
- Only works with TGW (not Virtual Private Gateway)
- Each VPN connection: 2 tunnels x 1.25 Gbps = 2.5 Gbps
- ECMP spreads traffic across all VPN tunnels attached to TGW
- Example: 4 VPN connections = 8 tunnels ≈ 10 Gbps aggregate
- Use for: high-bandwidth VPN when DX is not available or as DX backup with more bandwidth
7. TGW Multicast
- TGW supports IP multicast (one-to-many network delivery)
- Create multicast domains on TGW and register member ENIs
- Use for: financial market data distribution, video streaming, cluster communication
- Rare on the exam but good to know: "multicast on AWS" = TGW multicast
8. Complete Hybrid Connectivity Decision Table
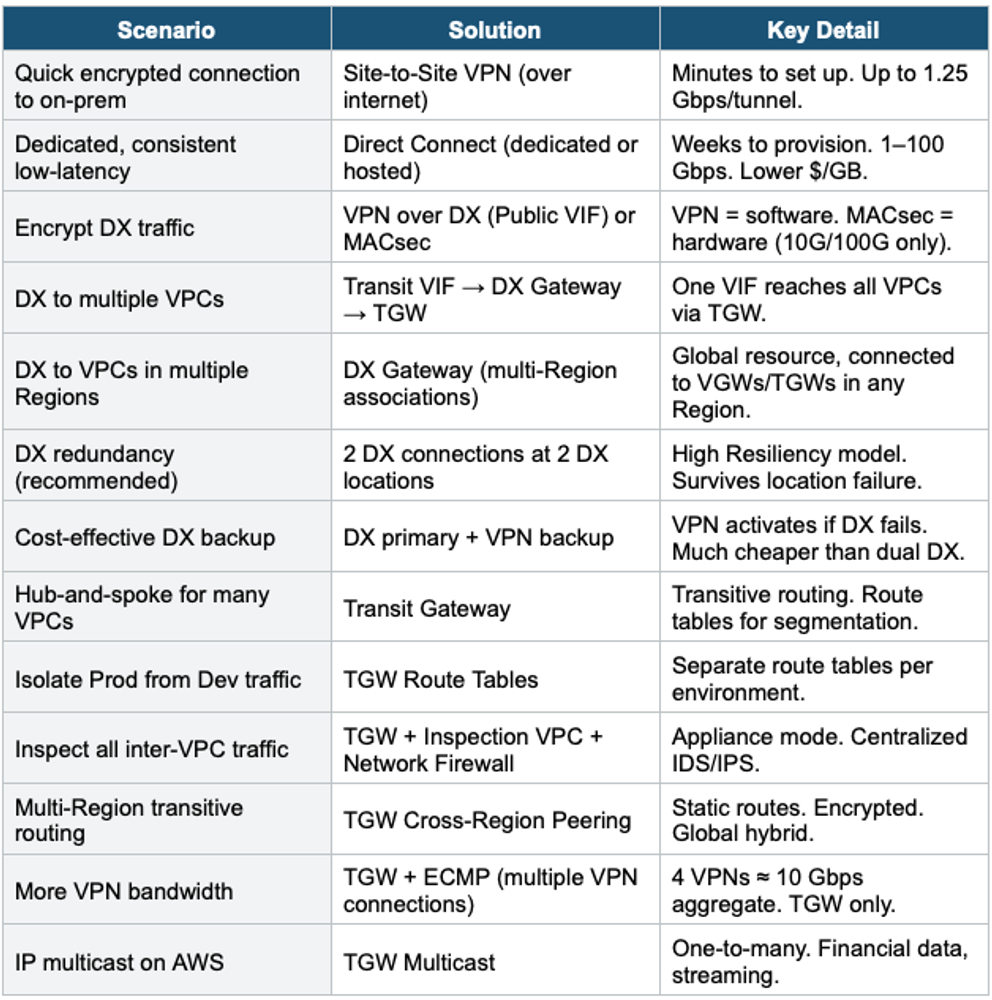
Exam Tip Hybrid Networking: "Dedicated private to AWS" = DX. "Quick encrypted" = VPN. "DX to many VPCs" = Transit VIF + TGW. "DX multi-Region" = DX Gateway. "Encrypt DX" = VPN over DX. "DX backup" = VPN. "DX redundancy" = 2 locations. "Segment VPCs" = TGW Route Tables. "Inspect traffic" = TGW + Inspection VPC + Appliance Mode. "More VPN bandwidth" = TGW ECMP. "Cross-Region routing" = TGW Peering (static routes).